Outsourcing is an effective way to reduce costs and scale operations without expanding your in-house team. However, it also introduces risks that can affect your data, service quality, and long-term costs. Understanding these risks early helps you make informed decisions and build more resilient outsourcing relationships.
Research highlights the scale of the challenge. According to a recent report from Verizon, third-party involvement in data breaches rose 60% year over year, appearing in 48% of all breaches. The World Economic Forum’s cybersecurity outlook also reports that 65% of large companies consider third-party and supply chain vulnerabilities their greatest challenge, up from 54% a year earlier.
These findings underscore why evaluating and managing outsourcing risks should be a priority for businesses working with external providers.
So, what should you look out for when choosing an outsourcing partner? How can you protect your business? In this guide, we’ll explore 12 key outsourcing risks, from financial uncertainty and vendor lock-in to cybersecurity threats and compliance challenges. We’ll also cover practical ways to mitigate each risk and provide a due-diligence checklist to help you evaluate potential BPO companies before making a commitment, whether you’re outsourcing IT functions or customer service.
Key takeaways
- Outsourcing cuts costs, adds specialized skills, and fuels growth, but it brings financial, operational, security, and compliance risks.
- The 12 key risks: financial uncertainty, operational disruption, vendor lock-in, cyber threats, AI and data handling, compliance failures, reputational damage, quality problems, geopolitical instability, cultural differences, supply chain disruption, and communication gaps.
- Manage risk with clear contracts, measurable SLAs, regular reviews, strong security controls, contingency plans, and open vendor communication.
- Due diligence checks a vendor’s finances, security, compliance, quality, staffing, subcontractors, and exit readiness.
- Risks differ by function. IT work centers on IP and system access, while customer service, healthcare, finance, and marketing raise quality, privacy, regulatory, and brand concerns.
- Keep evaluating vendors after signing by reviewing evidence, performance metrics, and risk controls.
- Helpware manages risk with SOC 2 Type II, ISO 27001, and ISO 9001 certifications, HIPAA, GDPR, and PCI DSS compliance, 19 locations in 11 countries, dedicated QA teams, and real-time reporting.
- Structured vendor selection, contract safeguards, and continuous monitoring protect operations and build resilient partnerships
Top 12 Vendor Outsourcing Risks You Can Face in 2027
| Risk | Warning signs | How to reduce the risk |
|---|---|---|
| Financial | Invoices exceed the quoted rates, and additional charges or change requests keep adding up. | Define rates, volume tiers, and change-order procedures in the contract. Set limits on annual price increases. |
| Operational | Backlogs grow, handoffs are missed, or staffing falls short during peak periods. | Agree on staffing and capacity plans, set attrition targets, and maintain a tested business continuity plan. |
| Vendor lock-in | The vendor is the only party that understands the processes, and switching providers would be costly or difficult. | Retain ownership of documentation, data, and tools. Define exit terms and transition support in the initial contract. |
| Cybersecurity | Accounts use shared credentials, access permissions are too broad, or the vendor cannot provide security audit reports. | Request SOC 2 Type II or ISO 27001 evidence, enforce role-based access and multifactor authentication, and review access regularly. |
| AI and data handling | Employees enter customer data into public AI tools, or the vendor uses client data to train models without approval. | Require written approval for AI tools, prohibit unauthorized model training on client data, and review AI-generated customer communications. |
| Compliance | The vendor cannot explain which regulations apply to the work or demonstrate how it meets them. | Identify applicable requirements, including HIPAA, PCI DSS, or GDPR, map them to specific controls, and conduct regular audits. |
| Reputational | Customer complaints point to inappropriate agent behavior, broken promises, or inconsistent service. | Document brand voice and escalation procedures, monitor reviews and social media mentions, and agree on how public complaints will be handled. |
| Quality | Quality assurance scores decline even though workload and service volumes remain steady. | Set clear quality criteria, review interactions regularly, and calibrate QA scorecards with the vendor. |
| Geopolitical | All outsourced work depends on one country or region that could be affected by political instability or policy changes. | Distribute delivery across multiple locations and maintain a tested plan for transferring work if a site becomes unavailable. |
| Cultural | Agents follow scripts without adapting to context, or employees hesitate to raise concerns and suggest improvements. | Provide joint onboarding and cross-cultural training, encourage open feedback, and review customer interactions together. |
| Supply chain | The vendor relies on subcontractors or other third parties whose security and reliability have not been assessed. | Request a list of subcontractors and other fourth parties, extend relevant security and continuity requirements to them, and identify backup suppliers. |
| Communication | Updates arrive late, time zone differences delay decisions, or urgent issues remain unresolved. | Agree on overlapping working hours, a regular reporting schedule, a designated contact on each side, and a channel for urgent issues. |
Financial risks
Outsourcing doesn’t always deliver the savings a business expects. Extra charges for training, transitioning work, technology licenses, overtime, or requests outside the original scope can quickly increase costs. Currency fluctuations also tend to make services more expensive when payments are made in another currency. Additionally, there’s the risk that a vendor facing financial difficulties may struggle to maintain service quality or end the partnership unexpectedly.
How to reduce financial risks
Before signing a contract, review the vendor’s financial health using a financial risk assessment. It’s also worth calculating the full cost of outsourcing, including setup, technology, and ongoing operating expenses, and comparing it with customer service outsourcing cost benchmarks.
Agree on pricing, volume tiers, and how additional work will be billed before the contract starts. Ask for audited financial statements or a credit report to assess the vendor’s financial stability. To avoid unexpected increases later, set a limit on annual price adjustments and specify how they will be calculated.
Operational risks
Operational risks include disruptions that interfere with the smooth integration of external services into the company’s processes. High staff turnover, system outages, and poor workforce planning can lead to service interruptions, delivery delays, and understaffing. Such operational disruptions in turn can have cascading effects on internal processes, productivity, and customer satisfaction.
Lack of vendor choice or failure to make proper capacity arrangements can lead to bottlenecks and prevent the company from achieving its objectives.
How to reduce operational risks
Controlling operational risks means detailed planning, establishment of a supplier pool, the use of a supplier portal for enhanced communication and coordination, and establishing a contingency plan to respond appropriately when unexpected eventualities arise.
You should also agree on staffing plans that account for forecast demand, set targets for staff attrition, and require the vendor to test its business continuity plan at least once a year. Ask how quickly the vendor can replace an agent who leaves the company to minimize service disruptions.
Vendor lock-in and loss of control
Vendor lock-in occurs when switching providers becomes so costly or complicated that staying with an underperforming vendor seems like the easier option. This often happens gradually. The vendor takes over procedures, manages the tools, and holds the data, while your internal team loses the knowledge needed to run the operation independently. Over time, this can also weaken your negotiating position.
You can also lose visibility into day-to-day operations if the vendor provides limited reporting. When you receive updates only once a month, problems may go unnoticed until they start affecting customers.
How to reduce vendor lock-in
To maintain control, retain access to the resources needed to transfer work to another provider, including process documentation, knowledge bases, call recordings, data exports, and administrator access to relevant platforms.
Include exit terms and transition support in the original contract, specifying how data will be returned and in what format. Keep an internal owner who understands the process in detail, and develop your outsourcing strategy with the flexibility to transfer work to another provider when necessary.
Cybersecurity risks
Giving a vendor access to your systems increases your exposure to cyberattacks. Recent IBM research identifies supply chain compromise, in which attackers gain access through a business partner, as the second most common initial attack vector after phishing. It also has the highest additional impact on breach costs, adding an average of $227,250. These breaches take an average of 258 days to identify and contain.
Outsourced operations often involve handling or exchanging confidential information, so a compromised vendor account can put your customers’ data at risk too. Attackers target vendors through phishing and ransomware because a single provider may have access to multiple clients’ systems and data.
How to reduce cybersecurity risks
To strengthen defenses and safeguard the confidentiality and integrity of shared data, organizations must cooperate closely with vendors to build a common commitment to the issue of cybersecurity.
Businesses must do their due diligence to ensure their systems and the vendors’ networks are secured with appropriate safety features.
Start by checking the vendor’s core security controls: multifactor authentication for accounts that access your data, permissions limited to each user’s role, encrypted devices and connections, and logs that your team can review. Ask for the vendor’s latest System and Organization Controls (SOC) 2 Type II report or ISO 27001 certificate, and review any exceptions or qualifications rather than relying on the summary alone. When an agent leaves the project or the company, revoke their access immediately. Review access permissions every quarter to ensure the data stays safe.
AI and data-handling risks
Outsourcing vendors increasingly use AI for tasks such as agent assistance, quality scoring, translation, and call summaries. While these tools can improve efficiency, they also introduce risks. An agent might enter customer details into a public AI chatbot, a vendor might use your call transcripts to train a model without your permission, or an AI-generated response might reach a customer without human review.
How to reduce AI and data-handling risks
Standard security questionnaires don’t always cover these issues in enough detail, so ask vendors specifically how they use AI, which tools they rely on, and how they protect your data. If a vendor cannot clearly identify the AI tools used to handle your information, treat that as a warning sign.
Require the vendor to disclose every AI tool used for your account and obtain written approval before any tool is introduced. Prohibit the use of your data to train vendor or third-party AI models without your explicit consent, and require human review of AI-generated content before it is sent to customers.
Compliance risks
Compliance risks in vendor outsourcing revolve around the potential non-adherence to legal and regulatory requirements. Failure to comply with industry standards and governmental regulations can result in legal repercussions and reputational damage.
Organizations must scrutinize potential vendors to ensure they align with relevant compliance standards, be it data protection laws or industry-specific regulations.
The specific requirements depend on your industry, the type of data you handle, and where your customers are located. Healthcare data is subject to the Health Insurance Portability and Accountability Act (HIPAA), which requires a business associate agreement with vendors that handle protected health information on behalf of covered entities. Payment card processing is governed by the Payment Card Industry Data Security Standard (PCI DSS). In the EU, the General Data Protection Regulation (GDPR) governs personal data, while the Digital Operational Resilience Act requires financial firms to manage risks associated with their technology providers.
The complexity of global compliance landscapes adds a layer of challenge, emphasizing the need for due diligence and clear contractual agreements that explicitly outline compliance expectations.
How to reduce compliance risks
Managing compliance risks involves ongoing monitoring, periodic audits, and fostering a culture of compliance within the outsourcing relationship to mitigate the potential fallout of regulatory non-compliance.
Identify the regulations that apply to your operations and translate them into specific requirements for the vendor. Verify that the vendor has the necessary controls in place, and use regular audits to check ongoing compliance. For regulated work, choose a provider with relevant expertise and safeguards, such as a HIPAA-compliant call center for handling patient data.
Reputational risks
Reputational risks are inherent in vendor outsourcing and can be as detrimental as they are elusive. A vendor’s actions and performance directly affect the brand image of an organization.
An outsourcing partner can negatively impact a company’s image through negative press, service failures, or ethical lapses. In today’s age of speedy communications and social media monitoring, the reputational fallout can be quick and heavy.
How to reduce reputational risks
Taking control of reputational risks means choosing vendors with a solid track record, establishing firm measures for their performance, and establishing an open gateway of communication where concerns can be expressed and problems resolved.
Document your brand voice and escalation procedures, monitor customer reviews and social media mentions regularly, and agree in advance on how the vendor should respond to public complaints.
Quality risks
The main quality risks in vendor outsourcing concern the situation in which those products or services offered by external partners are in some way sub-standard in quality. This can not only lead to customer dissatisfaction but also result in costs incurred by rectification and damage to the organization’s image. Vendor compliance with quality standards is an important consideration.
How to reduce quality risks
The sure way to reduce quality risks is to set clear quality standards in contracts, hold frequent performance evaluations, and create a climate of continuous improvement. Tough oversight, following industry standards, and joint work with suppliers to remedy problems and improve quality as soon as they arise are essential to keeping quality up in outsourcing.
Track quality alongside your service-level agreements (SLAs), since missed SLAs can signal declining performance before customers start complaining.
Geopolitical risks
Vendor outsourcing faces an additional layer of complexity in the form of geopolitical risk, which includes political instability, trade disputes, and adjustments in government policies.
The stability of outsourcing relationships can be affected by events occurring on the world stage, such that the delivery of services or goods is delayed. Organizations have to do in-depth geopolitical risk assessments. They need to take into account the political climate and economic conditions of the regions where their vendors are.
Companies are already adjusting. Recent PwC research found that half of organizations are changing how they manage vendor, third-party, and supply chain risk as geopolitical rivalry reshapes cyber threats.
How to reduce geopolitical risks
A main way to defend against threats from geopolitical shocks is the diversification of vendor portfolios, building contingency plans for possible geopolitical disruptions, and keeping up to date with international affairs.
Such uncertainties necessitate strategic foresight and adaptability. Only through being able to anticipate geopolitical challenges can organizations take preventive steps to ensure the survival of outsourced operations.
You should always consider political stability and labor laws when choosing your BPO outsourcing destination. Distribute delivery across multiple countries and maintain a tested plan for transferring work if one location becomes unavailable.
Cultural risks
Differences between organizations and external partners in cultural norms, communication styles, and business practices are among the risks of vendor outsourcing. Cultural factors can have a big impact on cooperation, teamwork, and overall project success.
Language barriers, differences in work attitudes, and different ways of thinking about how to solve problems can all lead to miscommunication and cause outsourced services to break down. This also means raising cross-cultural awareness, promoting candid communication, and developing cross-cultural training programs for both sides.
How to reduce cultural risks
A shared understanding of each other’s cultural nuances builds a cooperative environment for outsourcing and improves the effectiveness of the outsourcing relationship. Recognizing and seeking to bridge cultural differences is not just a defensive risk management move; it is an essential piece in the design of strong, united alliances that span nations and cultures.
With that in mind, provide joint onboarding that covers your customers, products, and brand voice. Encourage agents to flag unclear policies, and review a sample of customer interactions together to identify misunderstandings early.
Supply chain risks
Supply chain risks arise when disruptions affecting a vendor’s suppliers or subcontractors interfere with the delivery of outsourced services. These disruptions can stem from raw material shortages, transportation problems, geopolitical events, or overreliance on a single supplier.
Because outsourcing vendors often depend on other companies to deliver their services, problems further down the supply chain can affect your operations too. Assessing these dependencies helps you identify potential vulnerabilities and prepare for disruptions before they affect service delivery.
How to reduce supply chain risks
Proactive monitoring across the supply chain is essential for detecting problems early. Diversifying suppliers and assessing their reliability can help businesses keep outsourced operations running when a supplier becomes unavailable.
Ask for a list of the vendor’s subcontractors and other third parties involved in delivering your services. Require relevant security and business continuity requirements to extend to these parties. Map critical supplier dependencies and establish backup arrangements for those that could disrupt service delivery if they become unavailable.
Communication risks
Vendor outsourcing communication risks stand out as key considerations, including the problems arising from differences in language, time zones, and styles of communication. In today’s connected global business world, the ability to communicate effectively is essential for successful collaboration.
Misunderstandings arising from language barriers may affect project clarity and performance. Differences in time zones may lead to longer response times and coordination problems. Also, different communication norms and standards affect the interpretation of feedback and project updates.
How to reduce communication risks
Communication risks can be reduced only by defining communication protocols, by using such technologies as real-time collaboration for communication, and, where appropriate, supplementing them with language and cultural training.
Establishing regular, open lines of communication and transparent reporting structures between outsourcing organizations and their partners is essential to the development of a cooperative, positive working relationship. Proactive management of communication risks leads to better understanding, higher morale, and common goals among outsourcing partners.
You should establish overlapping working hours, a regular reporting schedule, and a designated contact on each side. Agree on a dedicated channel for urgent issues so time-sensitive requests aren’t delayed by time zone differences or missed emails.
Reduce outsourcing risks with Helpware
With 20+ years in business, we understand the complexities of outsourcing and how to manage its risks. Our client relationships last five years on average, and we maintain 90% CSAT across engagements. Reach out to us to discuss your outsourcing needs.
Outsourcing Risks by Function
The 12 outsourcing risks described above can affect businesses differently depending on the function being outsourced. IT and software development projects, for example, require clear intellectual property (IP) ownership terms, strong code quality controls, and restricted access to production systems. Customer service and call center operations, meanwhile, call for consistent quality standards, effective agent retention, and a tone that reflects your brand.
Regulated and brand-facing functions bring additional responsibilities. Healthcare outsourcing needs safeguards for protected health information and compliance with applicable regulations, while outsourcing marketing necessitates clear brand guidelines, approval processes, and data ownership terms. The table below outlines the main risks associated with each function and the safeguards to establish with your vendor.
| Function | Key risks | Safeguards |
|---|---|---|
| IT and software development | IP ownership disputes, inconsistent code quality, and unauthorized access to production systems | Clear IP assignment clauses, regular code reviews, and restricted production access |
| Customer service and call centers | Declining service quality, high agent attrition, and inconsistent brand voice | QA scorecards, attrition targets, and joint calibration sessions |
| Healthcare | Exposure of protected health information and HIPAA violations | A business associate agreement, HIPAA training records, and audit logs |
| Finance and payments | Payment card data exposure, fraud, and regulatory violations | A clearly defined PCI DSS scope, segregation of duties, and [PCI-compliant call center](https://helpware.com/cx/services/pci-compliant-call-center) controls where applicable |
| Marketing | Inconsistent brand messaging, gaps in consent management, and unclear data ownership | Documented brand guidelines, approval workflows, and written data ownership terms |
Outsourcing Risk Mitigation Strategies
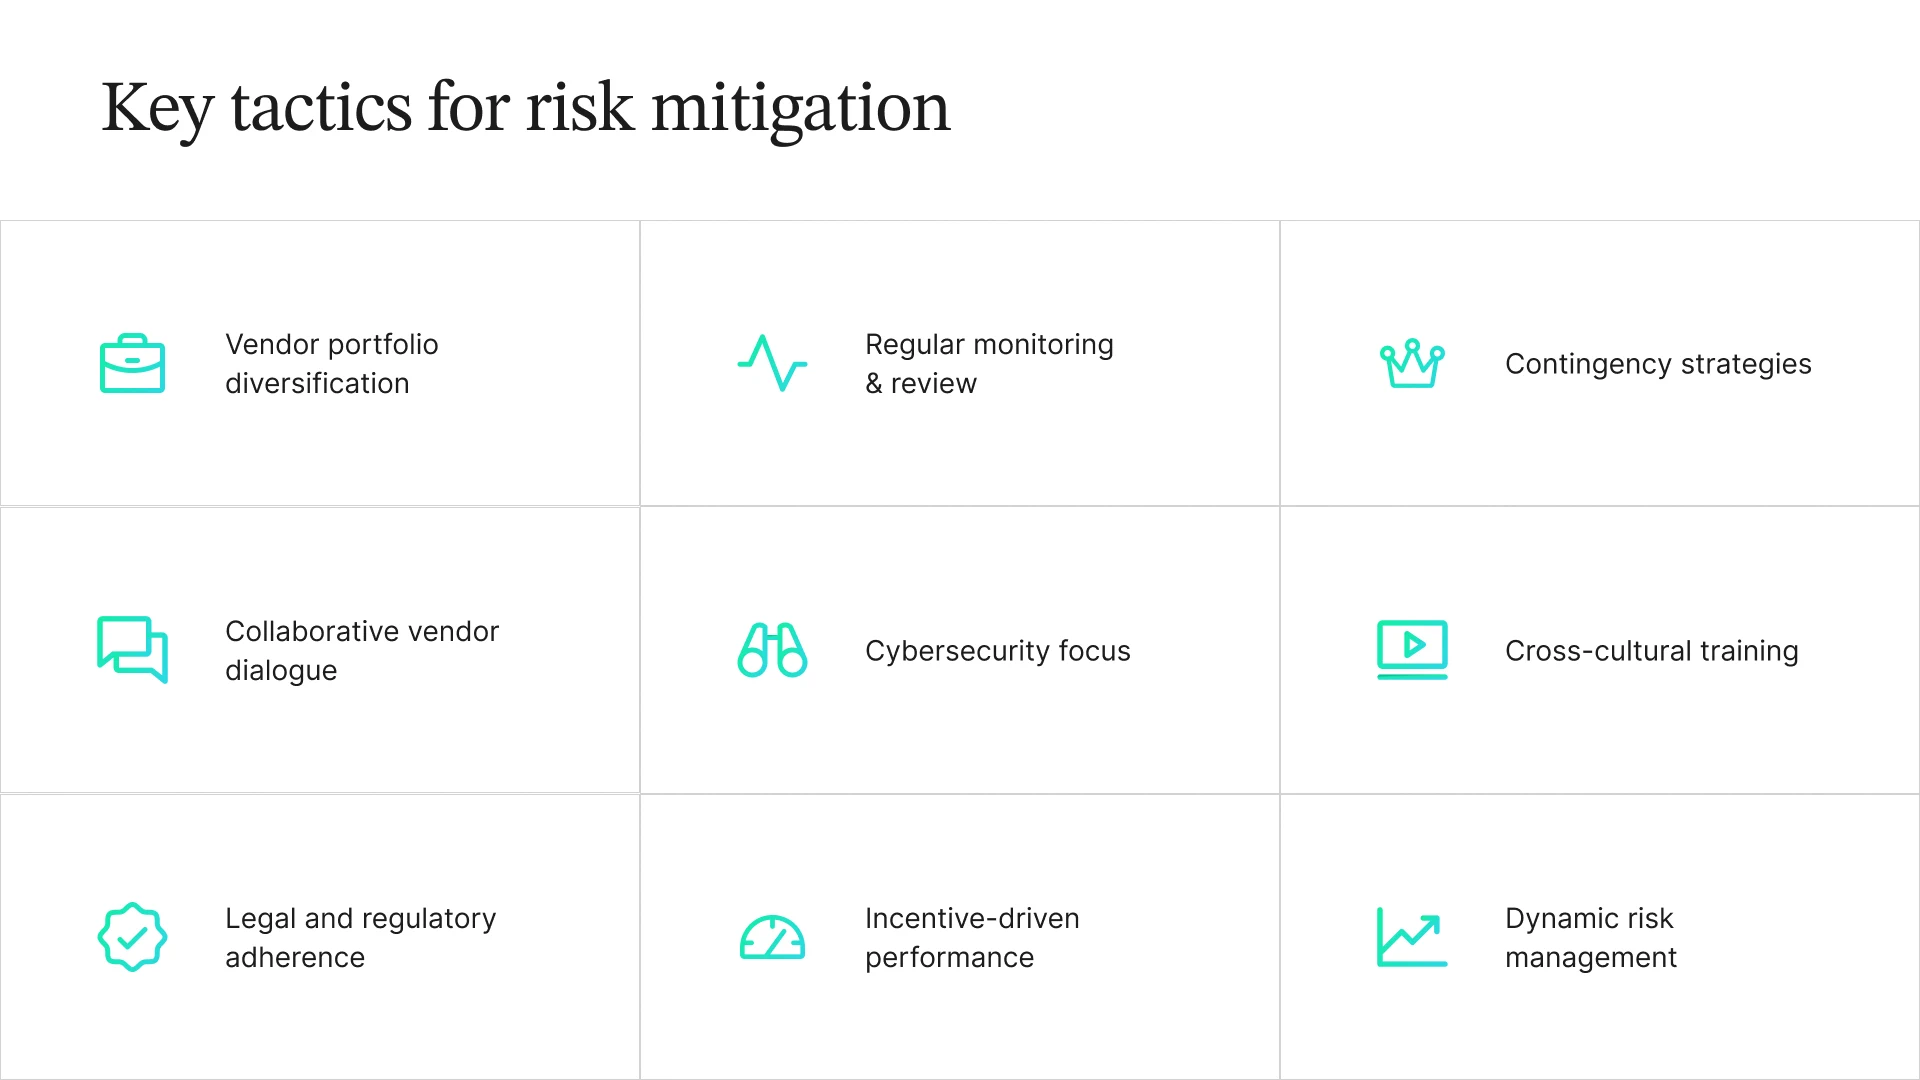
Managing the differing vendor risks demands a proactive and strategic attitude. To protect their interests and to make sure that outsourcing arrangements are successful, organizations need to deploy firm risk mitigation plans. These strategies span financial, operational, cybersecurity, and cultural dimensions. A comprehensive risk mitigation plan involves:
Robust contractual agreements
Develop detailed contracts outlining roles, responsibilities, and performance expectations. Clearly define key performance indicators (KPIs) and establish mechanisms for addressing non-compliance. To support this process, you can use customizable templates available on platforms like Freshdox, tailored to your specific objectives.
Diversification of vendor portfolios
To minimize the impact of any potential disruptions, avoid placing too much dependency on a single vendor. Diversify vendor portfolios to keep risks under control and build overall robustness.
Continuous monitoring and evaluation
Establish evaluation indicators and develop ongoing monitoring mechanisms to follow up on vendor performance. Through regular evaluation, potential risks can be detected in time, which allows specialists to handle them effectively.
Contingency planning
Develop a business continuity plan with the vendor that covers system outages, sudden volume spikes, site closures, and vendor failure. Test the plan at least annually and clearly define who has the authority to activate backup arrangements.
Open and collaborative communication
Create open channels of communication between organizations and vendors. Invite regular updates, feedback, and brainstorming sessions.
Investment in cybersecurity
Strengthen cybersecurity defenses to prevent data breaches and unauthorized access. Regularly review and update security controls to address evolving cyber threats.
Cultural training and understanding
Cultural training must be provided to teams to increase cross-cultural understanding and cooperation, reducing cultural risks.
Legal compliance assurance
Build compliance checks into the due diligence process to make sure vendors abide by legal and regulatory requirements. Regular audits should provide further assurance of ongoing compliance.
Performance-based incentives
Contracts with performance-based incentives will help to motivate vendors to reach or exceed agreed-upon standards. This gives incentives and ensures consistently high quality.
Adaptive and proactive risk management
Prepare an adaptive risk management strategy taking into account future risks. Through aggressive risk management, organizations will be able to quickly respond to challenges and take advantage of opportunities, and this will result in long-term success in outsourcing relationships.
A holistic and adaptable risk mitigation strategy considers the unique challenges of each outsourcing relationship, promoting resilience and sustained success in the dynamic landscape of vendor partnerships.
Vendor Due Diligence: How to Find the Right Outsourcing Partner
Before committing to an outsourcing provider, take time to assess its financial stability, security practices, service quality, and ability to handle disruptions. The questions below can help you identify potential risks, verify the vendor’s claims with supporting evidence, and address any gaps in the contract before work begins.
| Area | Questions to ask | Evidence to request | What to include in the contract |
|---|---|---|---|
| Financial stability | Can you support our account throughout the contract term? | Audited financial statements or a credit report | Termination rights if the vendor’s financial position deteriorates significantly |
| Security | How do you control access to our data and systems? | A current SOC 2 Type II report or ISO 27001 certificate | A security incident notification deadline and the right to audit relevant controls |
| Compliance | Which regulations apply to our work, and how do you meet their requirements? | Relevant compliance documentation and training records for requirements such as HIPAA, PCI DSS, or GDPR | A business associate agreement or data processing agreement, as applicable |
| AI use | Which AI tools will process our data, and how will that data be used? | A list of AI tools used for the account and a written data-use policy | Restrictions on using our data to train AI models without written approval |
| Quality | How do you measure service quality and report performance? | Sample QA scorecards and SLA performance reports | Clearly defined SLAs, reporting requirements, and service credits where appropriate |
| Business continuity | How would you maintain service if a delivery site or critical system became unavailable? | A business continuity plan and results from the latest test | Recovery time targets and procedures for transferring work to a backup site |
| Staffing | What is your staff attrition rate, and how quickly can you replace departing team members? | Attrition rates and average time to fill vacant positions | Minimum staffing levels and designated team leads |
| Subcontractors | Which subcontractors or other third parties will be involved in delivering our services? | A list of subcontractors and other relevant third parties | Requirements for subcontractors to follow applicable security, compliance, and continuity obligations |
| Exit and transition | How would we transfer the work to another provider, and what data and documentation would we receive? | A sample transition plan | Data return requirements, handover support, transition timelines, and exit fees |
| References and track record | Can you connect us with clients who have outsourced similar work? | Client references and relevant case studies | A pilot period with clearly defined success criteria, where appropriate |
Due diligence should continue even after the contract is signed. Review key documents and performance evidence at least annually, reassess the vendor’s risk profile at each renewal, and follow up on any gaps or changes that could affect the partnership.
How Helpware Manages Outsourcing Risks
Outsourcing should help your business move forward, not introduce new risks. Helpware combines proven security standards, flexible global delivery, and transparent performance management to give you greater control over your outsourced operations.
Our SOC 2 Type II, ISO 27001, and ISO 9001 certifications, backed by a compliance program covering HIPAA, GDPR, and PCI DSS, help protect your data and support your compliance requirements. With delivery capabilities across 19 locations in 11 countries on four continents, you can distribute workloads across onshore, nearshore, and offshore teams to build a more resilient operation.
You also get visibility into performance through dedicated quality assurance teams and real-time reporting dashboards. With support in 45+ languages, the flexibility to start with a 30- to 60-day pilot, and client partnerships lasting more than five years on average, Helpware gives you a practical way to scale while keeping quality, accountability, and long-term stability in focus.
Wrapping Up
Outsourcing can help your business reduce costs, access specialized skills, and scale operations, but those benefits depend on choosing the right partner and managing the relationship well. Financial uncertainty, service disruptions, cybersecurity threats, compliance gaps, and quality issues can all undermine the value of outsourcing if they aren’t addressed early.
The best way to manage these risks is to make due diligence part of your vendor selection process. Assess each provider’s financial stability, security controls, service quality, staffing, and business continuity plans. Then put clear expectations, measurable SLAs, reporting requirements, and exit provisions in the contract. Once the partnership begins, continue reviewing performance and risk controls to catch problems before they affect your business.
At Helpware, we combine established security and quality standards, flexible global delivery, and transparent performance reporting to help businesses build reliable outsourcing operations. Whether you’re planning to outsource customer service or scale an existing team, we can help you identify the right delivery model for your needs.
Ready to explore outsourcing with greater confidence? Contact Helpware to discuss your goals and find an approach that works for your business.